A supervised final-year engineering development project combining a full-stack freelancing marketplace with AI decision assistance and blockchain payment escrow.
A running research project leveraging Large Language Models (LLMs) to detect complex software vulnerabilities in source code through fine-tuning and AST-based prompt engineering.
Syed Muhammad Irtaza Shahid(SP23-BSE-156)Muhammad Waleed(SP23-BSE-134)Muhammad Muneeb Azhar(SP23-BSE-125)
PythonPyTorchHugging Face TransformersTree-sitterLLMs
A running software security project building a scalable token-based semantic code clone detection platform to capture Type-3 and Type-4 clones across large open-source repositories.
Ali Muhammad(SP23-BSE-032)Ali Murtaza(SP23-BSE-033)Hafiz Muhammad Shams ul Huda(SP23-BSE-067)
A running research project developing an automated patch optimization engine powered by LLMs that synthesizes and verifies security patch suggestions for vulnerable code snippets.
A multi-modal web-based AI screening platform combining vision analytics, behavioral questionnaires, and machine learning models for early screening of autism spectrum and psychological disorders.
Completed biomedical signal processing system utilizing audio sensor processing and machine learning to detect nocturnal sleep apnea events in real time.
Completed research project capturing hierarchical Abstract Syntax Tree and Control Flow Graph structures to recommend software architectural improvements.
Completed computer vision healthcare system utilizing deep convolutional networks for automated skin lesion segmentation and dermatological risk classification.
Extract vulnerable code from patch files at function, file, and component levels, analyse repair patterns, and build a reusable benchmark for vulnerability research.
Measure cloned-code and dependency ratios across related software systems and multiple versions of the same system, using Linux kernel releases as an empirical case study.
Generate valid and faulty test inputs for complex data processing systems using constraints and mutation operators, reducing the cost of manual input-space exploration.
BS Software Engineering and BS Computer Science students interested in FYP supervision at COMSATS University Islamabad, Lahore Campus should email Dr Junaid Akram with the following details:
Group member names and registration numbers
Current CGPA and transcript highlight
Selected FYP opportunity title or proposed original research topic
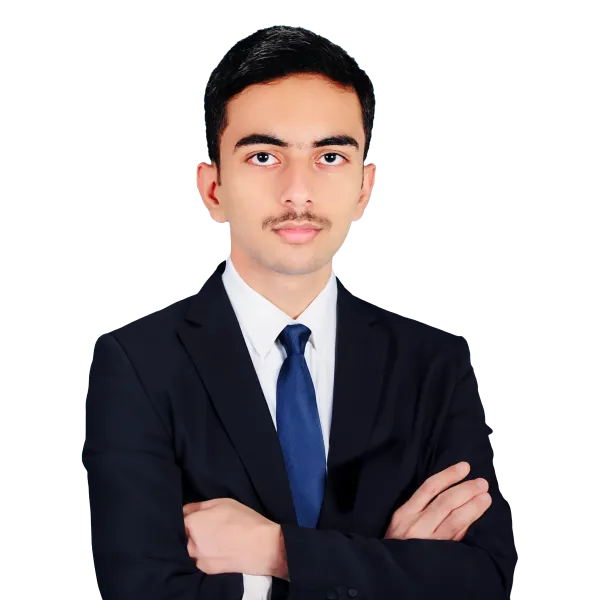 Ghulam Mujtaba (FA22-BSE-199)
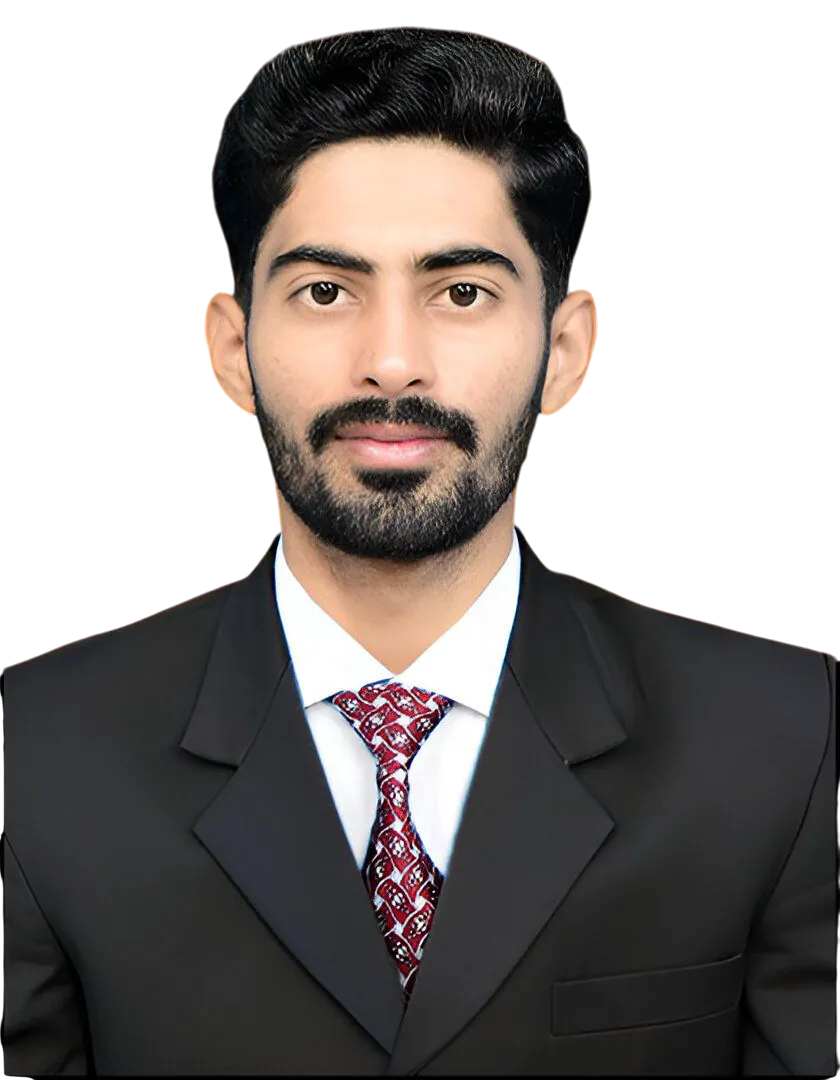 Muhammad Waqar Ul Mulk (FA22-BSE-153)